For businesses and charities
GDS Analytics acts as the data protection officer and part-time chief information security officer for organisations in financial services, hospitality, retail and the charity sector. You get one named adviser who learns how your organisation works, and a client portal that keeps the evidence in one place.
The problem
In many organisations, data protection belongs to the finance director, the head of IT or the company secretary, on top of everything else. That works until a client sends a security questionnaire, an insurer asks for evidence, or a breach starts the 72-hour clock.
Where you appoint a DPO, Article 37 of the UK GDPR expects expert knowledge of data protection law, and Article 38 expects them to report to your highest level of management.
Supplier due diligence, client audits and cyber insurance renewals all want evidence of how you protect data, not a statement that you do.
Someone has to own the risk register, set priorities and explain them to the board. Few smaller organisations can justify a full-time chief information security officer.
What we do
Take either service on its own, or both together under one retainer.
We act as your named DPO under Articles 37 to 39 of the UK GDPR, or as your data protection manager where a DPO is not required. That covers policies, your record of processing, DPIAs, subject access and other rights requests, breach decisions and regular reports to your board.
Security strategy, the risk register, policies and board reporting, from an adviser who works at board level. We answer the security questionnaires your clients send and prepare you for their audits.
A health check against the UK GDPR and the Data (Use and Access) Act 2025, and a gap analysis against Cyber Essentials, each with a prioritised plan and a short summary for your board.
Containment, the decision on whether to notify the ICO within 72 hours, communications with the people affected, and the lessons learned afterwards.
We handle the compliance and IT audit requests that enterprise clients and their auditors send, so your own team can stay on customer work.
If you are based outside the UK or the EU, GDS Analytics Limited and GDS Analytics (EU) Limited can act as your representative under Article 27. About representation
How it works
Every retainer includes the GDS client portal and supplier monitoring at no extra charge.
What clients say
Ensuring that GAIL’s remained compliant with data protection legislation was a significant task, so we considered a variety of options to help us in this regard. We decided to use the Data Protection Officer as a Service provided by GDS Analytics, as they could demonstrate and have subsequently delivered the technical and legislative ‘know how’ to meet our governance requirements and improve our cyber security posture. Their cost-effective services are professionally delivered by a helpful and supportive team.
As a software and data management business, Gather would routinely be required by enterprise clients with global operations to conduct compliance and IT audits. Due to the specialised, and complex, nature of these audits we chose to outsource and appoint an external DPM service. Following a tender process we appointed GDS Analytics. The team at GDS Analytics were thorough, responsive and devised a clear roadmap for compliance in addition to handling all client audit requests, both direct and via client appointed external auditors. Their work released internal resources to focus on customer projects and ensured we remained compliant, increasing customers and reducing on-boarding costs. Their rates are competitive and the team are personable, professional and became an extension of our team. I would recommend them highly.
Your adviser
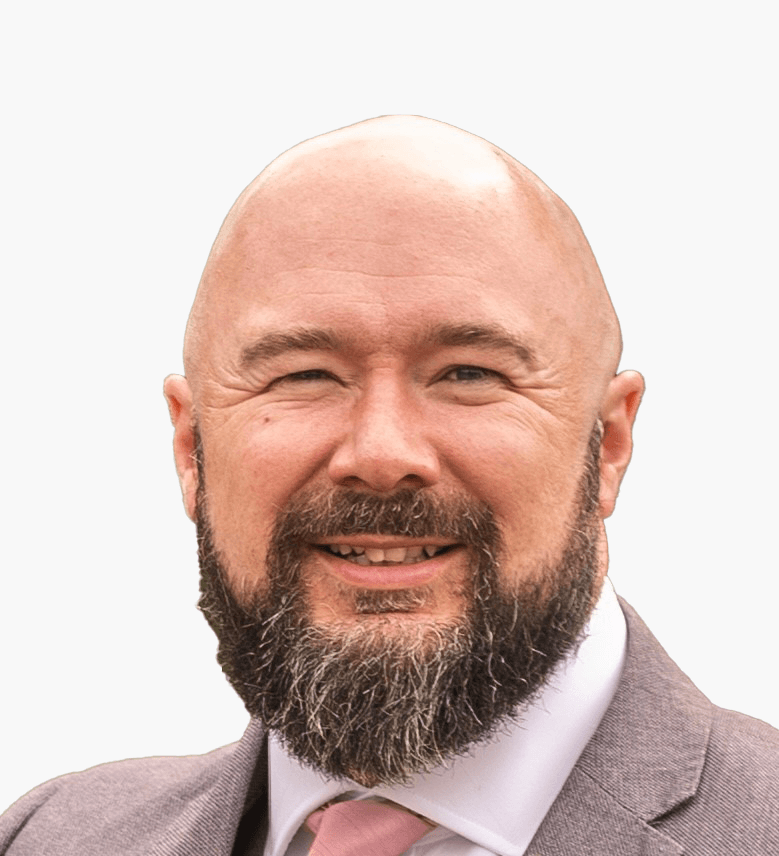
Director, GDS Analytics
Marc is the named data protection officer and fractional chief information security officer for our clients. He has supported schools and businesses since the UK GDPR came into force in 2018, and works where technical security meets the boardroom: turning risk into decisions that governors, boards and finance directors can act on.
He holds three of the most widely recognised certifications in information security and audit: CISSP (since 2018), CCSP and CISA.
Questions
Under Article 37 of the UK GDPR you must appoint one if you are a public authority, or if your core activities involve regular and systematic monitoring of people on a large scale, or large-scale processing of special category or criminal offence data. Many organisations that are not required to appoint one still choose to, or appoint a data protection manager instead. We can tell you which applies to you.
The job of a chief information security officer, part time: owning the security strategy and risk register, setting priorities, reporting to the board and dealing with clients, auditors and insurers on your behalf.
Yes. The client portal and supplier monitoring are included in every retainer at no extra charge.
No. Independent schools are a speciality, but we work with businesses and charities in financial services, hospitality, retail and other sectors.
A free, no-obligation 30-minute consultation on your current position and the two or three things worth fixing first.
© 2026 GDS Analytics. All rights reserved.